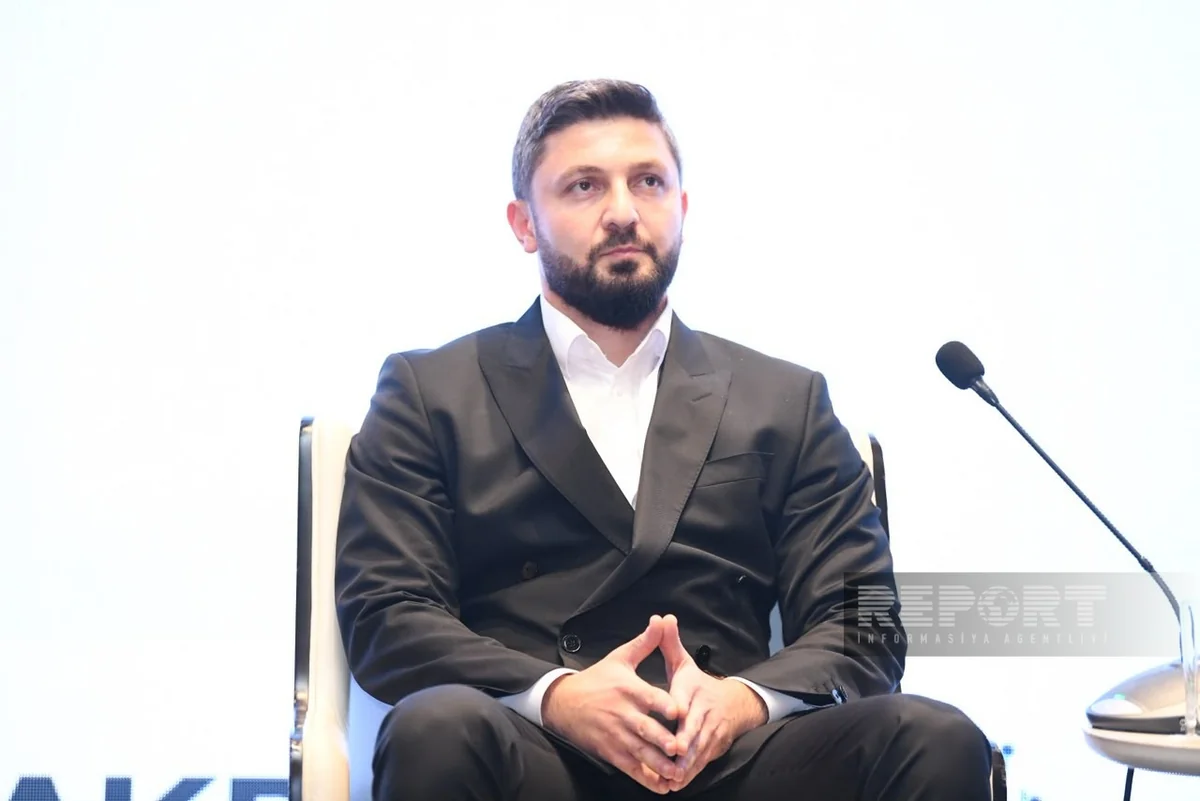
Failing to submit an initial cybersecurity incident notification to the Central Bank of Azerbaijan within the prescribed deadline constitutes a regulatory breach for financial institutions, said Abid Alasgarzada, deputy director of the bank’s Information and Cybersecurity Department.
Report informs that he was speaking at the 12th Investment and Sustainable Development in Microfinance Conference, organized by the Azerbaijan Microfinance Association (AMFA) in Baku.
He said reporting requirements set specific deadlines that organizations must observe.
“An initial notification must be submitted within four hours. Detailed information is not expected in the initial report. It should simply explain what happened-in short, what we know, what we do not know and when we expect to have comprehensive information.
“A detailed report must then be submitted within five days. These requirements are fixed,” he said.
Alasgarzada noted that submitting the initial notification on time is essential even if the full details of an incident remain unknown. Some organizations may consider notifying the Central Bank only after fully investigating its causes and consequences, but this approach breaches regulatory requirements.
“An institution may mistakenly believe it should wait two days, gather all the information, establish what happened and why, and then provide the Central Bank with a comprehensive account. In fact, that approach itself violates the requirement. Even if all the details are not yet known, the institution must submit an initial notification on time,” he emphasized.
He added that using the designated communication channels is also essential. Organizations must comply with both reporting deadlines and the prescribed procedures for transmitting information.